An ISMS provides your organization with a framework for information security. In day-to-day work, the key is for people to understand this framework: What information needs to be protected? Why do certain rules apply? And how does one's own work contribute? What The Hack! enriches your awareness program with collaborative exchange and active engagement.


ISO/IEC 27001 outlines the requirements for an information security management system, or ISMS for short. People and organizational processes are just as much a part of information security as technical safeguards. Awareness connects this framework with everyday work.
INSIGHT INTO WHAT THE HACK!
What seems obvious to one person may raise questions for another. In team play, these differences become the starting point for learning: participants exchange arguments and agree on a shared answer.

Insight into the team play of What The Hack!
This creates an opportunity to discuss information security as part of your awareness program. The follow-up context can establish the connection to your internal policies and reporting procedures.

Select focus area

Play together
Participants engage with safety issues, discuss their assessments, and make joint decisions.

Pick up on results

Actively involve employees. Participants engage with safety topics instead of merely consuming content.
Make assessments open for discussion. Through exchange, it becomes clear which arguments support a decision and where questions remain unanswered.
Make security communication relatable. Use the shared gaming experience to address your internal policies and responsibilities.
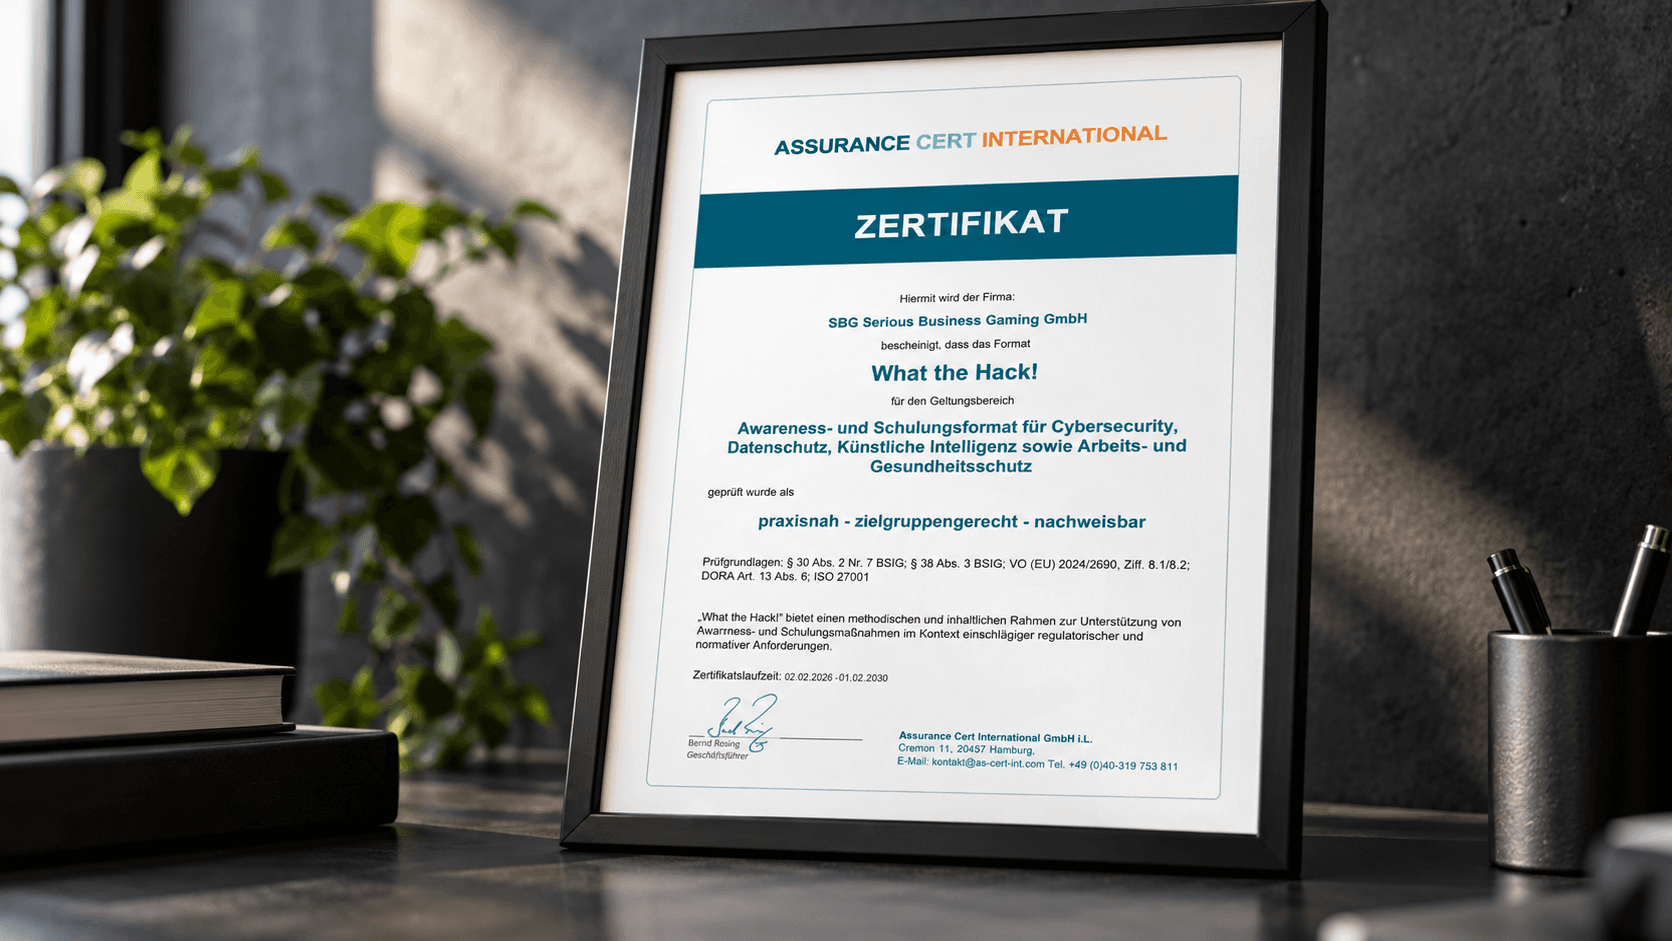
Document participation and results. Certificates of participation and game evaluations support the documentation of your measure.
Create recurring occasions. Use selected campaigns to revisit information security throughout your program.