What The Hack! externally audited | BSIG, DORA & ISO 27001

THE GAME BEHIND THIS BLOG
One team. One shared goal: catch the hacker. What The Hack! is our serious game for security awareness. Employees discuss security questions and agree on an answer as a team.
What The Hack! Receives Certificate: Serious Gaming for Security Awareness
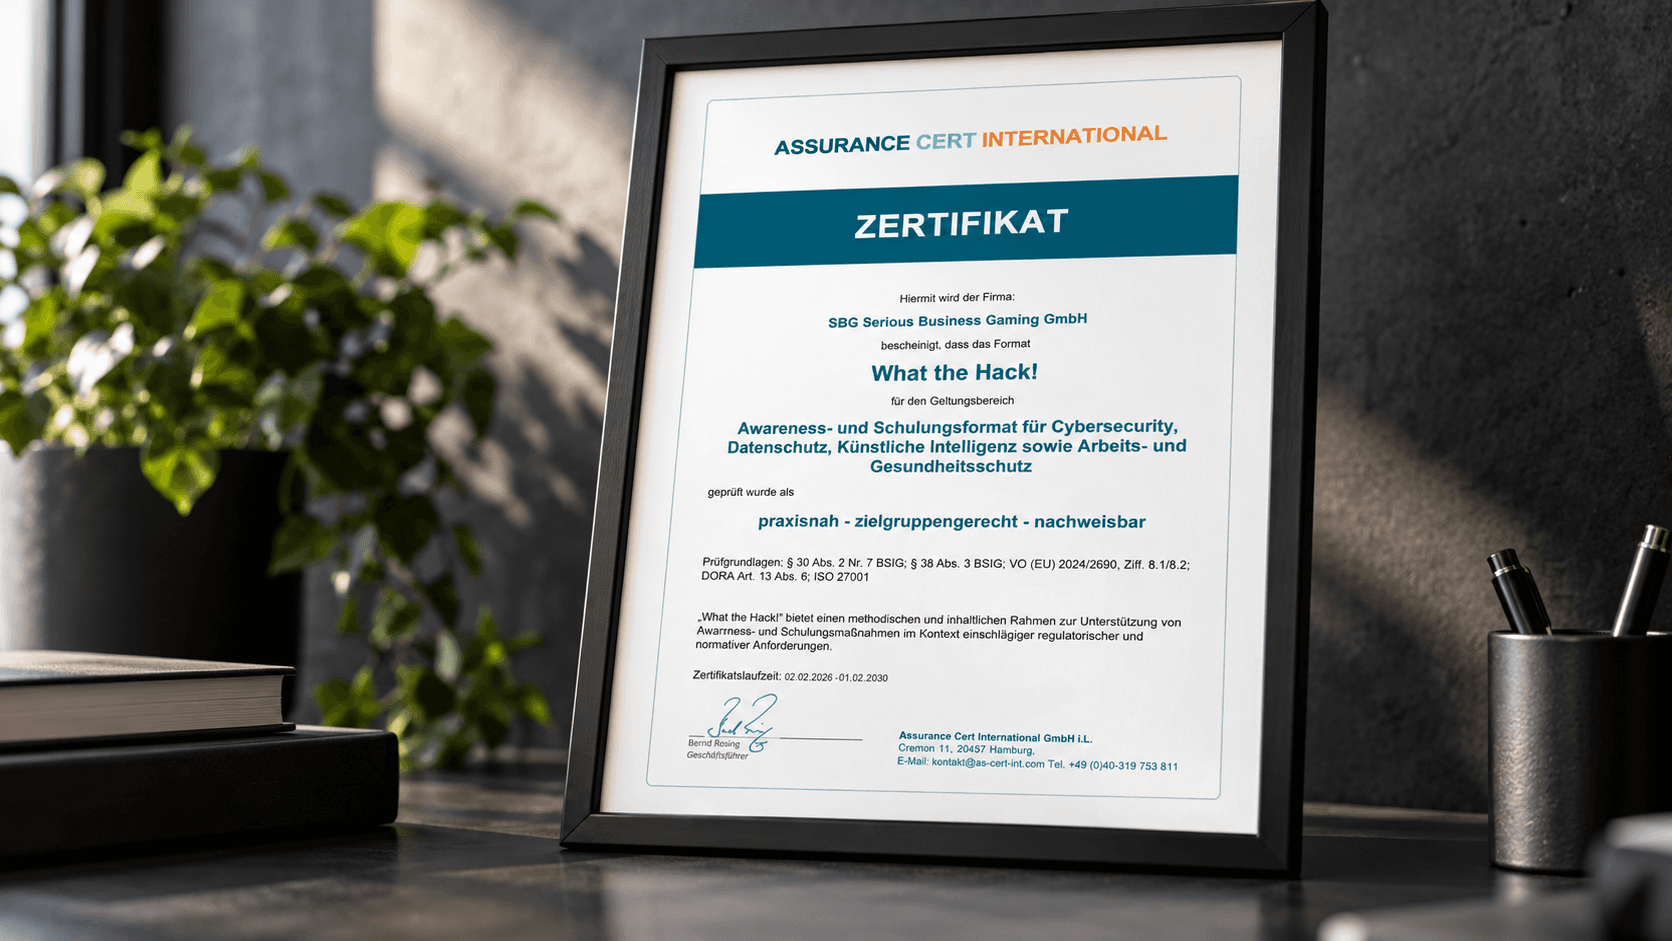
Can cybersecurity training be fun, technically demanding, and support companies with regulatory requirements all at the same time? At What The Hack!, the answer is: Yes. Our serious business game was externally evaluated by Assurance Cert International and rated as practical, target-group-oriented, and verifiable.
The evaluation criteria include, among others, the German BSI Act (BSIG), DORA, and ISO 27001. For us, this is more than just a certificate. It is another building block showing that game-based learning has a place where risks are real and requirements are high.
Externally Evaluated: What the Certificate Confirms
The assessment refers to What The Hack! as an awareness and training format for cybersecurity, data protection, artificial intelligence, as well as occupational health and safety. It confirmed a methodological and content framework that can support companies with corresponding awareness and training initiatives.
The certificate was issued on February 2, 2026, and is valid until February 1, 2030.
BSIG, NIS2, DORA, and ISO 27001: What Does This Mean for Companies?
Companies dealing with NIS2 and the requirements of the BSIG, DORA, or ISO 27001 need more than documented policies. Employees must recognize risks, develop confidence in taking action, and know how to respond in critical situations.
The external evaluation highlights that What The Hack! provides a methodological framework to support such training measures. It does not replace an individual compliance audit, nor does it represent a standalone certification according to the aforementioned standards.
Serious Business Gaming: Where Game-Based Learning Meets Serious Topics
“That's just a game.” We occasionally encounter this reaction when companies hear about serious business gaming for the first time. Understandably so: cybersecurity, data protection, and compliance are topics involving real risks, economic damages, and responsibility.
However, anyone who experiences What The Hack! quickly realizes that a playful approach by no means contradicts technical depth.
In our awareness game, employees jointly discuss realistic scenarios from areas such as phishing, social engineering, data protection, or compliance. They have to consider different perspectives, justify decisions, and agree on an answer as a team.
This sparks the exact conversations for which time is often lacking in daily work. Uncertainties come to light, experiences are exchanged, and supposedly self-evident behaviors are questioned. Game mechanics and competition create motivation, while the substantive discussion remains front and center.
Our Standard: A Culture of Security Instead of Mere Training Records
A completed mandatory training session does not yet constitute a lived security culture. What matters is whether employees better assess risks in everyday life, speak up in critical situations, and act more consciously.
In our gaming sessions, we regularly witness how initial skepticism turns into intense discussions, surprising insights, and shared ambition. That is precisely where we see the potential of serious business gaming: abstract security requirements turn into concrete decisions that teams talk about with one another.
This can support companies in reducing human risks, strengthening collaboration, and pursuing their security and compliance goals more effectively. Digital evaluations and certificates of completion complement this approach by providing documentation of the training measures.
Why We Have Our Awareness Format Externally Evaluated
We do not want the term “game” to leave any doubts about the technical quality of our training format. That is why we make our methodology transparent and also have it reviewed by external parties.
The certificate is not a scientific proof of efficacy, nor is it a guarantee of a successful security culture. However, it confirms key qualities of our format and provides an additional foundation for our clients' trust.
Our conviction remains: Playful learning is not the antithesis of professional security awareness. It can be a crucial lever to engage people, build a security culture, and turn knowledge into actual action.

Your Contact Person
Thorben Steenmanns
Chief Gaming Officer & Head of Sales
What if your next awareness training remained a positive experience in the minds of your colleagues?
A vibrant security culture is the most powerful defense against hackers. I help you build yours—using our serious business game What The Hack! for cybersecurity, data protection, and compliance.


